

Agent Foskett Investigates Microsoft Security
30 Real-World Investigations Using Microsoft Defender XDR, Microsoft Sentinel, KQL and Microsoft Security Copilot
Security incidents rarely arrive as complete stories. They arrive as fragments: a sign-in, a process, an email, a permission change, a line of telemetry that does not quite fit. This book follows Agent Foskett through 30 investigations and shows how evidence becomes a timeline, a timeline becomes a theory, and a theory must survive the facts before it becomes a conclusion.
Now available worldwide on Amazon. The first edition was published on 1 September 2026 and is available in Kindle, paperback and hardcover formats.
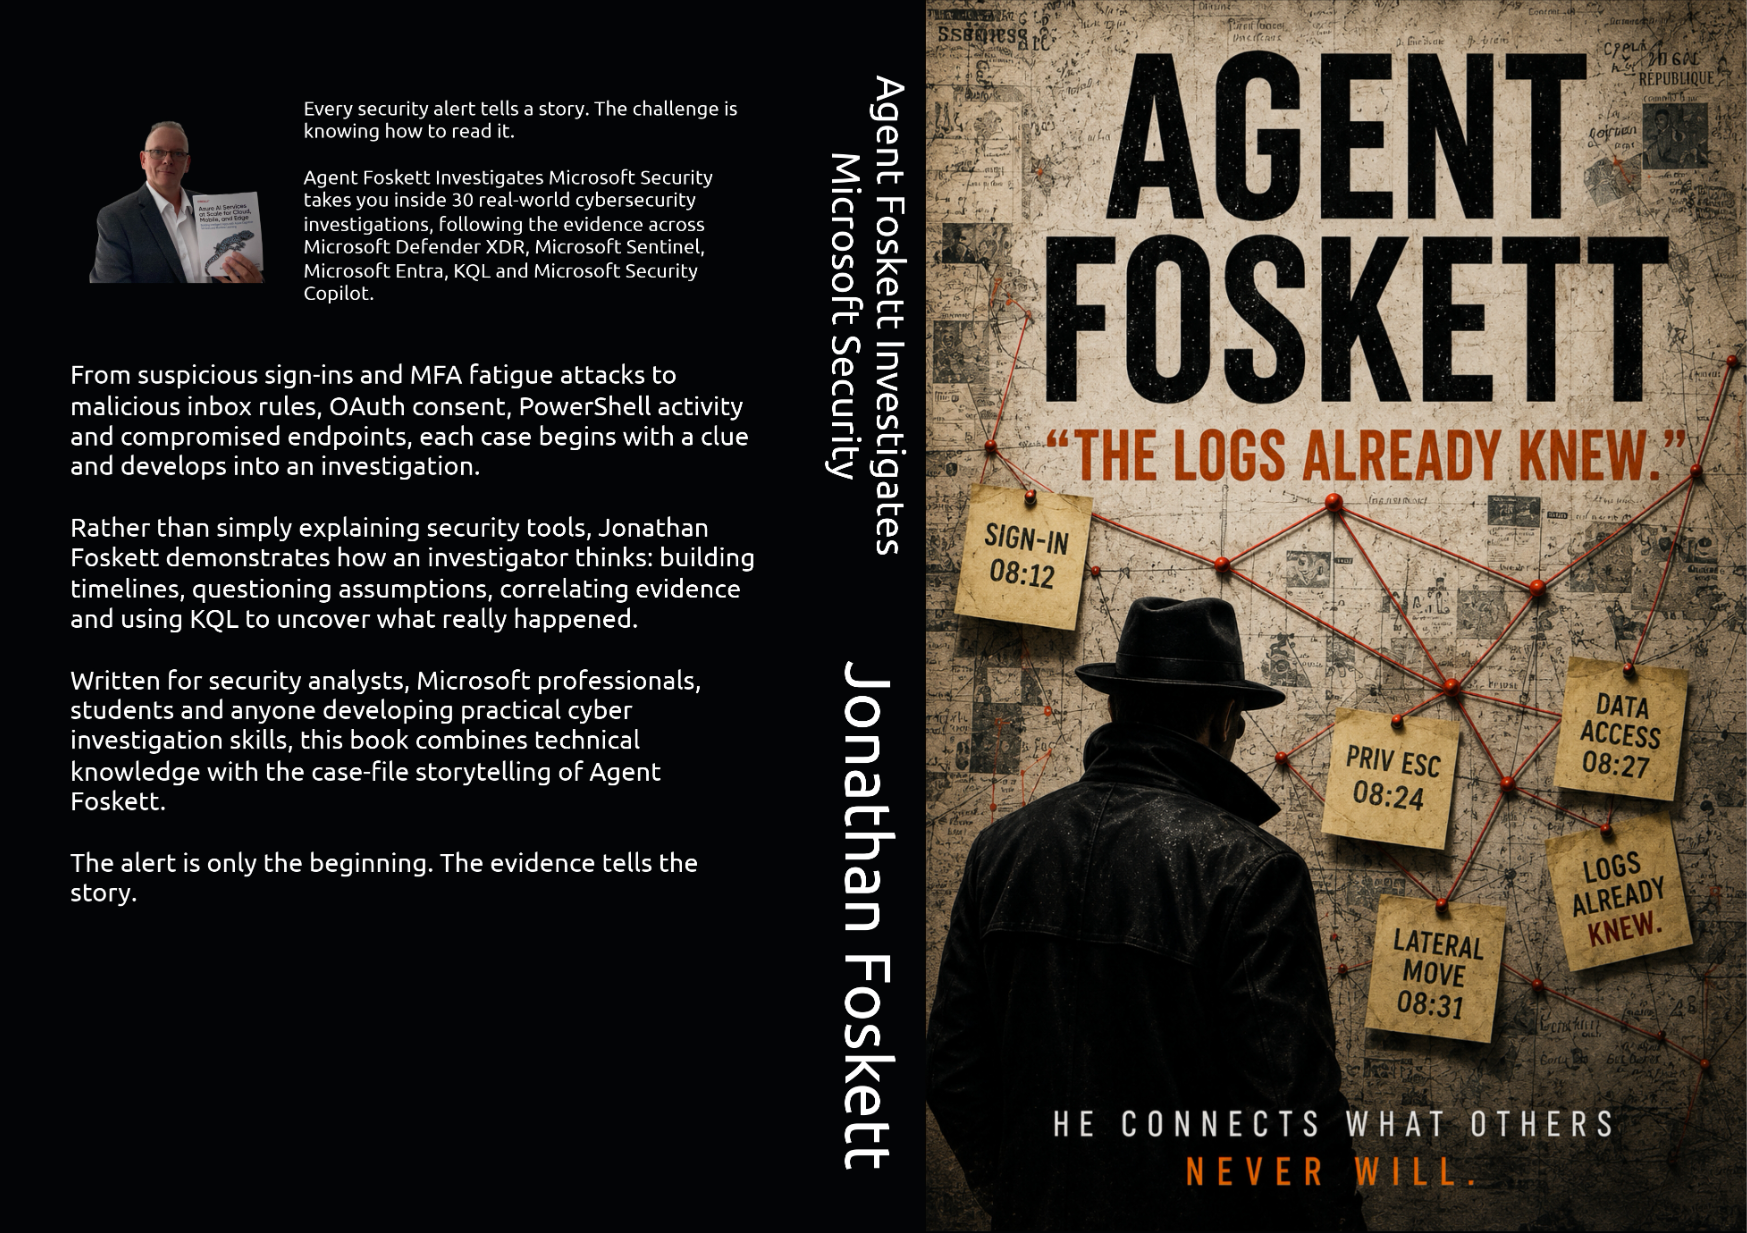
“The alert is only the beginning. The evidence tells the story.”
Not another software manual
30 investigations. One evidence-first approach.
Across 30 real-world investigations, Agent Foskett follows the evidence through identity, email, endpoints, cloud activity, privilege changes, persistence and AI-assisted security operations.
Microsoft Defender XDR, Microsoft Sentinel, Microsoft Entra, KQL and Microsoft Security Copilot appear throughout the investigations, but the technology is only part of the story. Every case comes back to the same investigative discipline: follow the evidence, build the timeline, challenge the theory — and ask what the logs actually prove.
Published on 1 September 2026, Agent Foskett Investigates Microsoft Security is available worldwide in Kindle, paperback and hardcover editions.
Inside the case files
